ABOUT VLOZ
We didn't build VLOZ to sell software. We built it because our own clients needed it.
VLOZ wasn’t dreamed up in a product meeting. It came out of Brea Networks — a Managed Service Provider and Managed Security Service Provider that’s been in the trenches of federal compliance since 2010, doing the actual work: configuring environments, writing SSPs by hand, sitting across the table from assessors, and watching small businesses nearly lose contracts because compliance took too long.
We got tired of watching that happen. So we built the tool we wished we’d had.
Founded on doing the work, not just advising on it
Brea Networks has operated as a full-service MSP and MSSP since 2010 — which means we don’t just consult on cybersecurity, we run it. We hold CMMC Level 2 certification, maintain 22 CFR ITAR compliance, and operate under a NIST SP 800-53 Rev. 5 (Moderate) framework ourselves. Our team includes personnel holding Top Secret clearance, so sensitive engagements never have to wait on a security review we can’t pass ourselves. We’re not describing controls from a textbook. We’re implementing, maintaining, and living inside the same requirements we’re asking you to meet.
That distinction matters. A lot of platforms in this space were built by people who’ve read the frameworks. VLOZ was built by people who’ve been assessed against them.
Built by an MSP, for the speed an MSP needs
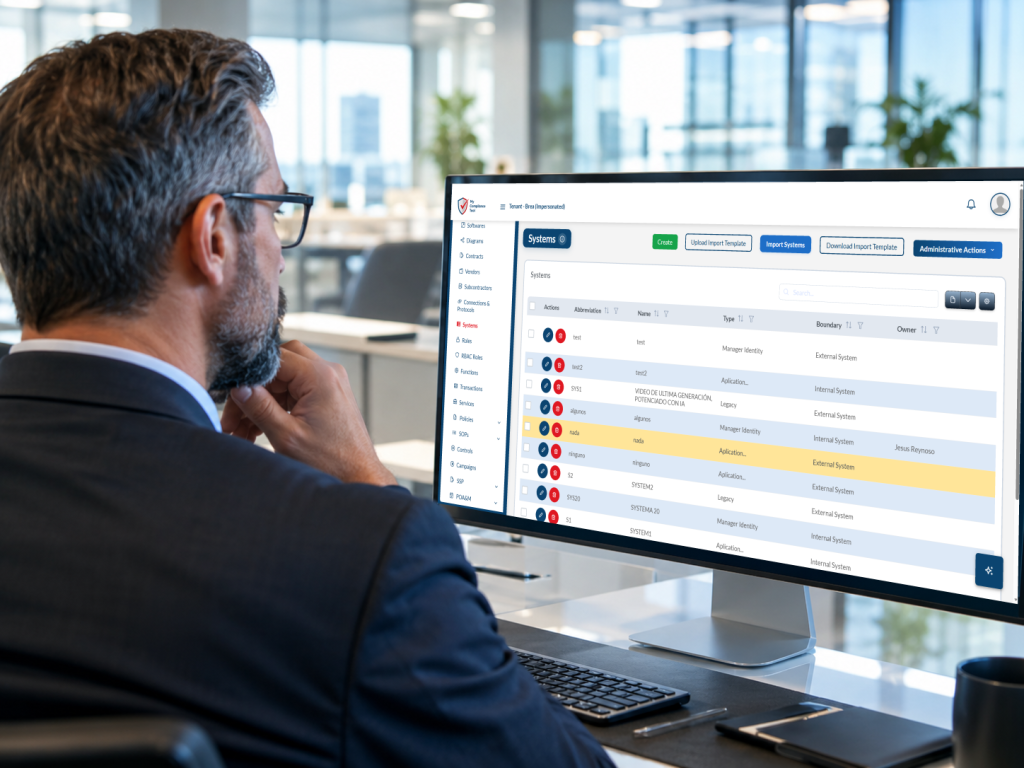
VLOZ software development began in 2019, born directly out of Brea Networks’ day-to-day work as an MSP/MSSP serving Defense Industrial Base clients. We needed a way to onboard and configure compliant environments faster than manual configuration would ever allow — so we built the automation ourselves, then kept building until it became a complete platform.
That’s the difference between VLOZ and a tool designed by a software company that later decided to enter the compliance space: VLOZ was pressure-tested against real client deadlines from day one, because those deadlines were ours too.
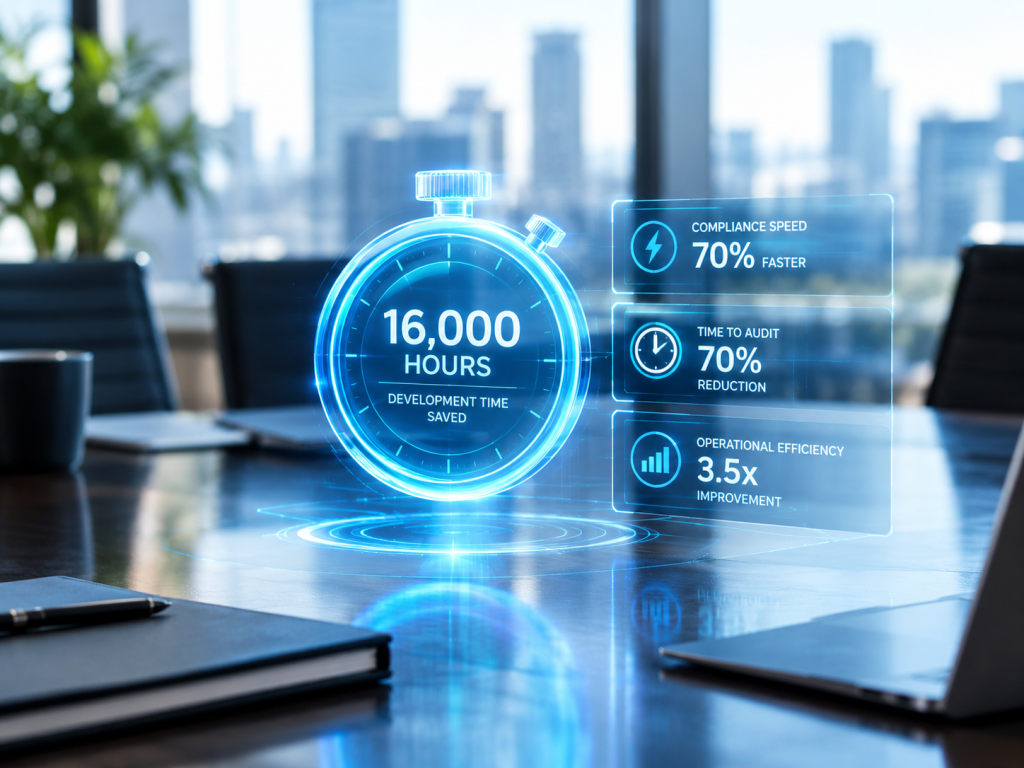
Since 2019, that’s translated into more than 16,000 hours of VLOZ software development — all in service of one goal: getting organizations to compliance without the months of delay that put contracts at risk.
Proven at every tier of the defense industrial base
Fifteen years of doing this work has put Brea Networks and VLOZ in front of nearly every kind of organization in the defense supply chain:
Small businesses
have used our full-service solutions to reach compliance
Defense Industrial Base contractors
run their compliance program on our platform
Ranked on the Inc. 5000
list of fastest-growing companies in IT Services
U.S. person operation support
And every bit of it — every deployment, every environment, every SSP, is delivered under 100% U.S. person operation support.
When you’re handling CUI and export-controlled data, who’s safeguarding your environment matters as much as what tool they’re using.
Why this matters to you
You’re not buying a compliance app from a startup that read the CMMC framework last quarter. You’re getting a platform built inside an MSP/MSSP that’s held ITAR compliance, operated under NIST 800-53 Rev. 5, and earned CMMC Level 2 certification itself — then turned fifteen years of doing that work into software that does it faster for you.
We’ve been on your side of the table. VLOZ is what came out of it.